Windows sign-in,
with a simple card tap.

Card-based sign-in to Windows 10 and Windows 11. In factories, warehouses and reception areas, several people often share one computer. ChipLogin makes sign-in easier for them and access easier to manage for you. We will assess whether your existing cards and readers can be used.

By card
Instead of typing passwords
No AD
No domain, no PKI
MIFARE
DESFire cards
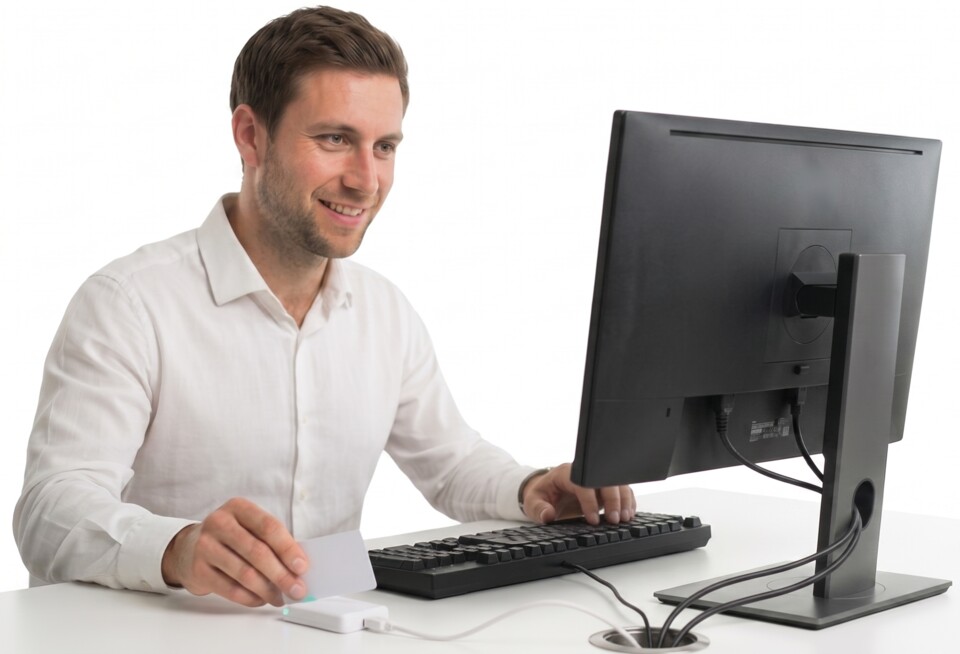
An over-the-shoulder view of an employee tapping an access card against a reader to log into a computer

Why ChipLogin for RFID login

Easier sign-in for employees and clearer access management for you.

Shared stations and shifts

Colleagues take turns at one computer. Each signs in with their own card, without sharing passwords.

Less password typing in business applications too

For supported applications, ChipLogin can fill in credentials after Windows sign-in too. We will discuss the specific software your team uses.

Encrypted with mTLS

Every station has its own certificate and generates its device key locally. Windows passwords are not displayed to users, and the password payload is protected by mTLS plus encryption to a one-time station key while in transit.

For standalone computers too

ChipLogin can also work on computers that are not joined to a company domain. We will check the deployment details for your environment.

Audit built right in

Who logged in, when, and on which computer. The visibility shared passwords never gave you.

Easy installation

ChipLogin software is installed on the computers. We will review the requirements and help plan deployment for your environment.

3 steps to RFID login

Once set up, everyday sign-in is a simple card tap.

1

Tap the card

The employee taps their DESFire card on the reader beside the computer. Before deployment, we check the card configuration and suitable readers together.

2

Secure verification

ChipLogin cryptographically verifies the DESFire card and its assigned user. Verification takes place on a standalone computer or over an encrypted connection to a server on your network.

3

Logged in

After successful verification, the employee signs in to Windows. There is no need to type a password or look for it on a sticky note.

DESFire cards for your operation

We support MIFARE DESFire. Already using these cards? We will check their configuration and your readers. A readable card number alone is not enough to grant access.

Cryptographic verification

MIFARE DESFire

Existing card assessment

Suitable reader selection

No cards yet? We will recommend suitable DESFire cards and readers. The proposal will specify the equipment and setup included.

Technical specifications

Installation
MSI package (GPO, mass deployment) or self-contained EXE
Operating system
Windows 10/11, Windows Server 2016+ (x64)
Infrastructure
with or without a domain · no PKI · no changes to Active Directory
Readers
standard USB readers — we'll verify compatibility with yours
Cards
MIFARE DESFire — existing cards assessed before use
Management
centrally from ChipLogin Server · also works standalone for small deployments

RFID login — frequently asked questions

We support MIFARE DESFire cards. Reading a card number alone is not enough — ChipLogin verifies the card cryptographically. If you already use DESFire, we will assess whether your cards can be used; their configuration and the readers matter too.
An NFC label alone does not mean a card is supported. ChipLogin supports MIFARE DESFire cards, not arbitrary NFC cards, tags or phones. We will assess your specific cards and readers.
No. ChipLogin installs as a Windows Credential Provider on each station. It doesn't touch Active Directory and works even on standalone computers that aren't joined to a domain.
No external PKI deployment is required. Communication between the station and the authentication server uses mutual TLS (mTLS); each station generates its device key locally and receives the certificate used for that connection.
ChipLogin runs on Windows 10 and Windows 11. It replaces the password prompt on the Windows login screen, while the user's actual Windows password remains intact.
Local computer sign-in does not require the internet. In standalone mode, verification takes place on the computer itself. With shared management, the computer needs a connection to your server on the company network.
We can include suitable readers and MIFARE DESFire cards in a proposal tailored to your operation. For existing DESFire cards, we first check their configuration and whether they can be used.

Let's look at your operation.

Tell us how people currently sign in to your computers. You do not need to know card types or technical specifications. We will work through the details with you.

Contact directly

Jakub Skoumal · Sales

or use the form below ↓

Please enter your name
Please enter a valid email
Please enter a message

By submitting, you agree to our privacy policy.

Thank you. We have received your message.

We will get in touch to discuss the next steps.